

Table of Contents
Share with network
Related Insights
Accurate financial reporting relies on effective oversight, accountability, and controls that can adapt as risks change. Fraud remains one of the most significant threats to financial integrity, exposing organizations to financial loss, regulatory scrutiny, and reputational damage.
At its core, fraud is an intentional act designed to obtain an unfair or illegal advantage through deception. It often occurs when pressure, opportunity, and rationalization converge. While Internal Controls over Financial Reporting (ICFR) are designed to reduce the risk of material misstatement, the increasing speed and sophistication of fraud require organizations to continuously evaluate whether their control environments remain effective.
Although public companies face specific reporting obligations, strong financial controls are critical for organizations of all sizes. Smaller and privately held organizations often operate with fewer resources, making them equally vulnerable to operational disruption and financial loss.
As a result, leadership teams must balance growth, innovation, and risk management while maintaining an internal control environment capable of preventing, detecting, and responding to emerging threats.
Perhaps one of the most significant implications of AI adoption is its impact on accounting and financial reporting processes. AI is rapidly increasing the scale, speed, and sophistication of fraud across financial processes. Rather than replacing traditional fraud schemes, it enhances them by making attacks more convincing, expanding their reach, and accelerating execution.
According to Feedzai's 2025 AI Trends in Fraud and Financial Crime Prevention report, more than half of fraud activity now involves AI, including deepfakes, synthetic identities, and AI-enabled phishing attacks.
These schemes are also reaching further into day-to-day operations. As organizations adopt AI within their own processes, they should assess the opportunities and risks it presents alongside overall organizational readiness. Historical controls were designed for human-driven activities and may not be sufficient to address the speed, scale, and complexity of AI-enabled environments.
As AI becomes more embedded in business processes, organizations need to move toward more proactive, data-driven, and scalable risk management. A strong AI control environment is built on traceability and transparency. When organizations can clearly understand how AI-supported decisions were made, what data was used, who was responsible, and what controls governed the process, they strengthen oversight, accountability, and trust.
In response, organizations are enhancing fraud prevention and detection through:
Modern fraud risk management requires integrated, intelligence-driven monitoring capabilities.
Leading organizations are leveraging AI to strengthen fraud detection and internal controls by identifying unusual transactions and behaviors, monitoring high-risk activities across financial processes, detecting emerging fraud patterns, analyzing structured and unstructured data for risk indicators, and prioritizing higher-risk activities for investigation and review.
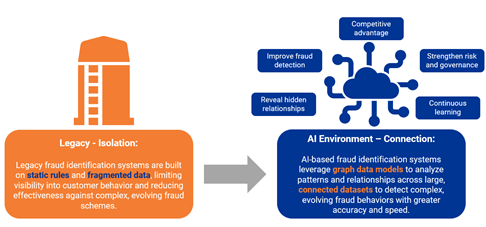
It is important to understand that technology alone does not manage risk. These capabilities hold only when someone owns them, challenges them, and independently validates that they are working as intended.
Effective fraud risk management begins with clear ownership, independent oversight, and accountability. Organizations are best positioned to manage fraud when risks are addressed at the point of activity, challenged through independent review, and monitored through an objective assurance process.
Strong governance frameworks share several core characteristics:
Ownership becomes visible in the controls an organization operates. Well-designed controls reduce fraud risk by strengthening oversight, accountability, and transparency across business processes. They help organizations prevent, detect, and respond to issues while improving the accuracy, reliability, and security of operations.
A strong internal control framework helps organizations reduce losses, maintain compliance, and build trust. Effective programs rely on multiple control types working together to prevent, detect, and respond to fraud risks. Examples of these control types include:
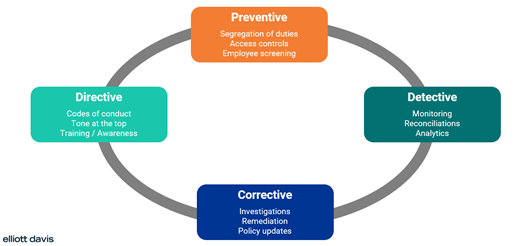
Preventive controls (stop issues before they occur):
Detective controls (identify issues after they occur):
Directive controls (guide behavior and decision-making):
Corrective controls (address and fix issues once identified):
Fraud risk will continue to evolve alongside the technology that enables it. Organizations that build governance in from the beginning, rather than retrofitting it after adoption, are more likely to manage risk effectively, maintain accountability, and support responsible AI adoption amid expanding use cases and growing third-party dependencies.
Approached this way, governance is not a constraint on innovation. It is what gives leadership confidence in its numbers, withstands the scrutiny of regulators and auditors, and earns the trust of the customers and stakeholders who depend on it.
Elliott Davis helps organizations assess, design, and enhance internal controls, AI governance programs, and fraud risk management capabilities to support compliance, strengthen oversight, and build stakeholder trust.
Interested in learning more about AI Governance? Watch the replay of our AI Governance Webinar to explore practical strategies for governing AI, managing emerging risks, and implementing controls that enable responsible and sustainable adoption.
Contact us today to schedule a fraud and internal controls readiness consultation.
The information provided in this communication is of a general nature and should not be considered professional advice. You should not act upon the information provided without obtaining specific professional advice. The information above is subject to change.

The OBBBA changes meal & entertainment deductions starting in the 2026 tax year. Most employer-provided meals will no longer qualify for deductions with a few specific exceptions. Explore next steps for employers.
Discover how the One Big Beautiful Bill Act (OBBBA) impacts financial institutions – from loan structures and compliance frameworks to tax incentives and product design. Learn key provisions and actionable strategies to stay compliant and seize new opportunities.