find your solution.
search for solutions by category, industries, insights, and people.
DO NOT PUBLISH
search for solutions by category, industries, insights, and people.


Table of Contents
Share with network
Related Insights
AI is already entering financial institutions through employee productivity tools, customer service platforms, fraud monitoring, credit analysis, compliance, financial reporting, and internal audit. In some cases, institutions may be using AI without formally implementing an “AI system” because AI capabilities are embedded within existing software or introduced through vendor updates.
Do existing controls still work when AI becomes part of the process? In many cases, the answer is yes, but their application may need to change. Governance, access, change management, operations, third-party management, and data management remain the foundation. Internal audit should identify where AI is being used, understand the impact, and determine whether the controls are appropriate for the risk.
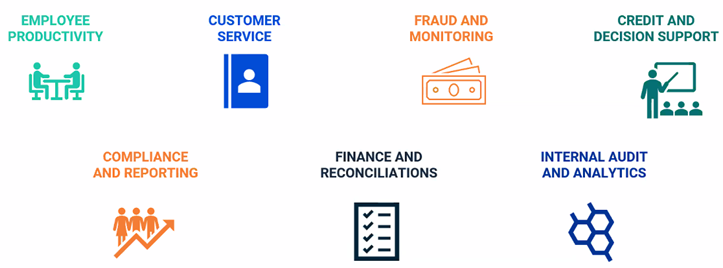
The first step is identifying where and how AI is used across the institution. Some applications are easy to identify, while others may enter a third party or employee use.
An AI inventory should identify approved tools, embedded features, vendor-provided services, and informal staff use. For each material use case, institutions should document its purpose, data involved, degree of automation, people or processes affected, and accountable owner
Internal audit should determine whether it is reasonably complete, trace use cases to appropriate approvals and controls, and confirm that responsibility is clearly assigned.
AI introduces new risk patterns, but familiar control principles still apply.
Existing IT and risk management controls provide a useful foundation for AI governance, including accountability, access, change management, operational monitoring, vendor oversight, and data protection. The question is whether those controls still address the specific risks created by each use case.
Controls should reflect potential impact. Drafting an internal document presents a different risk than AI influencing lending, fraud detection, customer communications, financial reporting, or movement of funds. As AI progresses from assisting an employee to recommending or executing an action, stronger controls may be appropriate.
Relevant factors include the sensitivity of the data, financial or regulatory impact, degree of automation, human review, and the ability to identify and reverse an error.
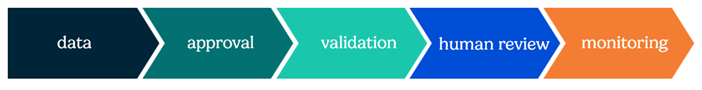
Controls should continue throughout the AI lifecycle.
Using an external AI service does not transfer responsibility for customer, operational, compliance, or reporting outcomes. Institutions should understand where data is processed and retained, whether prompts or outputs may train vendor models, which providers and subcontractors support the service, and how material changes are communicated.
Contracts and operating procedures should also address security, privacy, confidentiality, data ownership, incident notification, audit rights, service monitoring, and contingency planning. Internal audit should confirm that vendor risk reviews address the AI capability itself rather than assessing only the broader software product.
Internal audit can address AI through existing audits of lending, fraud, customer service, financial reporting, human resources, compliance, cybersecurity, and third-party risk, prioritizing AI uses with potential consequences for customers, regulatory obligations, the accuracy of financial statements, information security, material operations, or the movement of funds.
At Elliott Davis, our Digital Risk Services team can help financial institutions assess AI use, identify control gaps, evaluate governance and third-party risk, and incorporate AI considerations into existing internal audit and technology risk programs.
Contact us to discuss your institution’s AI governance, controls, and internal audit priorities.
The information provided in this communication is of a general nature and should not be considered professional advice. You should not act upon the information provided without obtaining specific professional advice. The information above is subject to change.
the
authors
related
insights

The importance of SOC 1 reports in financial services
Strengthen trust and compliance in financial services with a SOC 1 report, demonstrating robust internal controls and regulatory adherence. Learn how SOC 1 enhances credibility, mitigates risks, and sets your institution apart in a competitive market.

How CDP disclosure elevates your sustainability game
CDP disclosure is rapidly becoming a global standard for environmental reporting. As sustainability regulations tighten and supply chain transparency grows, businesses that engage with CDP can gain a competitive edge, enhance stakeholder trust, and prepare for evolving ESG compliance requirements.

Using tax accounting methods to improve current cash flows
Amid economic uncertainty and rising interest rates, businesses can optimize cash flow by leveraging tax accounting method changes. Learn how strategies like prepaid expense deductions, inventory valuation, and cost segregation can defer taxable income and improve liquidity.