


find your solution.
search for solutions by category, industries, insights, and people.
DO NOT PUBLISH
search for solutions by category, industries, insights, and people.


Table of Contents
Share with network
Related Insights
FinCEN’s April 2026 proposed anti-money laundering and countering the financing of terrorism (AML/CFT) program rule under the Bank Secrecy Act (BSA) puts effectiveness and risk-based decision-making at the center of program design. It would give financial institutions greater discretion to direct resources toward higher-risk customers and activities while incorporating FinCEN’s national AML/CFT priorities into program requirements.
The October 2025 interagency suspicious activity report (SAR) FAQs reflect a similar approach. Activity near the $10,000 currency transaction reporting threshold does not, by itself, require a SAR. Continuing-activity reviews are not mandatory, suggested timelines are not binding, and institutions need not document every decision not to file. However, institutions should not interpret this guidance as a reason to stop filing SARs on structuring, which could create serious legal and regulatory risk.
Instead, the message appears to be: Don’t file defensive structuring SARs without understanding the activity. A SAR is required when an institution “knows, suspects, or has reason to suspect” transactions are intended to evade currency transaction report (CTR) requirements.
When intent is unclear, investigate. Educate the customer, consider providing FinCEN’s CTR pamphlet, talk with frontline staff and the customer, and involve account officers or BSA/AML/CFT staff as appropriate. Never confirm or deny whether a SAR has been or will be filed.
Better information should drive the SAR decision, backed by policies, monitoring, investigations, and staffing that support sound judgment based on the institution’s risk.
Individual SAR decisions are one part of a broader risk-based approach. FinCEN’s national priorities provide a useful structure for evaluating BSA/AML/CFT risk:
Each should be evaluated against the institution’s customers, products, services, channels, and geographies. A risk assessment should explain where exposure exists, what controls address it, and why resources are concentrated where they are.
FinCEN’s 2026 alerts and analyses point to several active threats, including digital asset investment scam centers, Iranian sanctions evasion, fuel smuggling and tax evasion associated with Mexico-based cartels, the A7 network, human smuggling, and foreign-agent-directed transactions.
Financial institutions should use these publications to inform scenario design, targeted reviews, SAR activity coding, and staff training. Since criminal networks can use multiple payment methods, counterparties, legal entities, and jurisdictions, monitoring a single transaction type may miss the broader pattern.
Human trafficking and smuggling demonstrate the importance of evaluating transaction in context. Individual hotel charges, rental cars, peer-to-peer payments, remittances, or cash deposits may look ordinary. Together, they may warrant closer review based on:
BSA/AML, fraud, sanctions, and operations teams should have clear processes for sharing information when signals cross multiple functions.
Community banks are often the first and last line of defense. There is not a single stereotype of what elder financial exploitation looks like.
Possible indicators include new authorized signers, sudden large withdrawals, unfamiliar beneficiaries, unexplained account changes, unusual urgency, confusion about recent transactions, and reluctance to discuss account matters independently.
Front-line employees need a written escalation protocol that identifies who receives a concern, what information should be documented, and what happens next. Staff should know how to speak privately with a customer when appropriate and how state reporting or transaction-delay requirements apply.
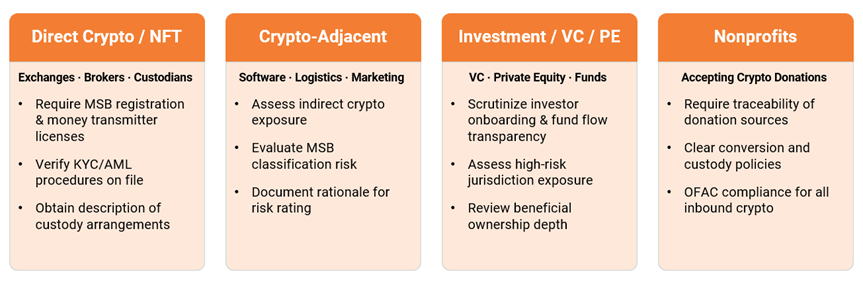
A financial institution can have material digital asset exposure without offering a crypto product. Customers may fund exchanges, receive proceeds from digital asset activity, operate crypto-related businesses, accept digital asset donations, or invest through funds with crypto exposure.
Customer due diligence should distinguish among four common profiles: direct crypto or NFT businesses; crypto-adjacent companies such as software, logistics, or marketing providers; investment funds; and nonprofits accepting digital assets. Relevant questions include who controls wallets, which exchanges and custodians are used, where counterparties are located, how funds move, and whether payment activity fits the stated business purpose.
Monitoring should consider velocity, source of funds, rapid movement across accounts or platforms, offshore destinations, high-risk jurisdictions, and unexplained changes in activity. The objective is a defensible risk assessment and monitoring approach tied to the institution’s actual exposure.
AI adds another dimension to fraud and identity risk. Generative AI can make forged documents and synthetic identities easier to produce at scale. Financial institutions may need layered identity controls, including document forensics, biometric verification, behavioral monitoring, and link analysis across accounts sharing device IDs, IP addresses, or other digital characteristics.
Elliott Davis helps financial institutions assess and strengthen BSA/AML/CFT programs, including independent reviews, fraud and AML model validation, model optimization, risk assessments, customer due diligence, transaction monitoring, and related governance. Our Financial Services professionals can help connect regulatory expectations and current illicit finance typologies to controls that fit your institution’s risk profile.
Contact our team to discuss your BSA/AML/CFT program, monitoring approach, or risk assessment.
The information provided in this communication is of a general nature and should not be considered professional advice. You should not act upon the information provided without obtaining specific professional advice. The information above is subject to change.
the
authors
related
insights