If there’s one thing our broad experience has taught us, it’s this: One size does not fit all.

Accounting Today
Accounting Today
Southeast’s fastest growing hubs as well as Bengaluru, India

Join us for a special live recording from the ONE building in downtown Greenville, SC, as we celebrated our 400th episode with a live audience! Drs. Milt Lowder and Drew Brannon reflect on their 9-year journey to 400 episodes and explore one of the most important topics in leadership: culture. What does it really take to build a great culture? They unpack clarity, values, feedback and learning, ownership, accountability, and belonging, sharing lessons from sports, business, and their own experiences. Most importantly, they challenge leaders to move beyond talking about culture and take intentional action to create the environment they want to be part of.
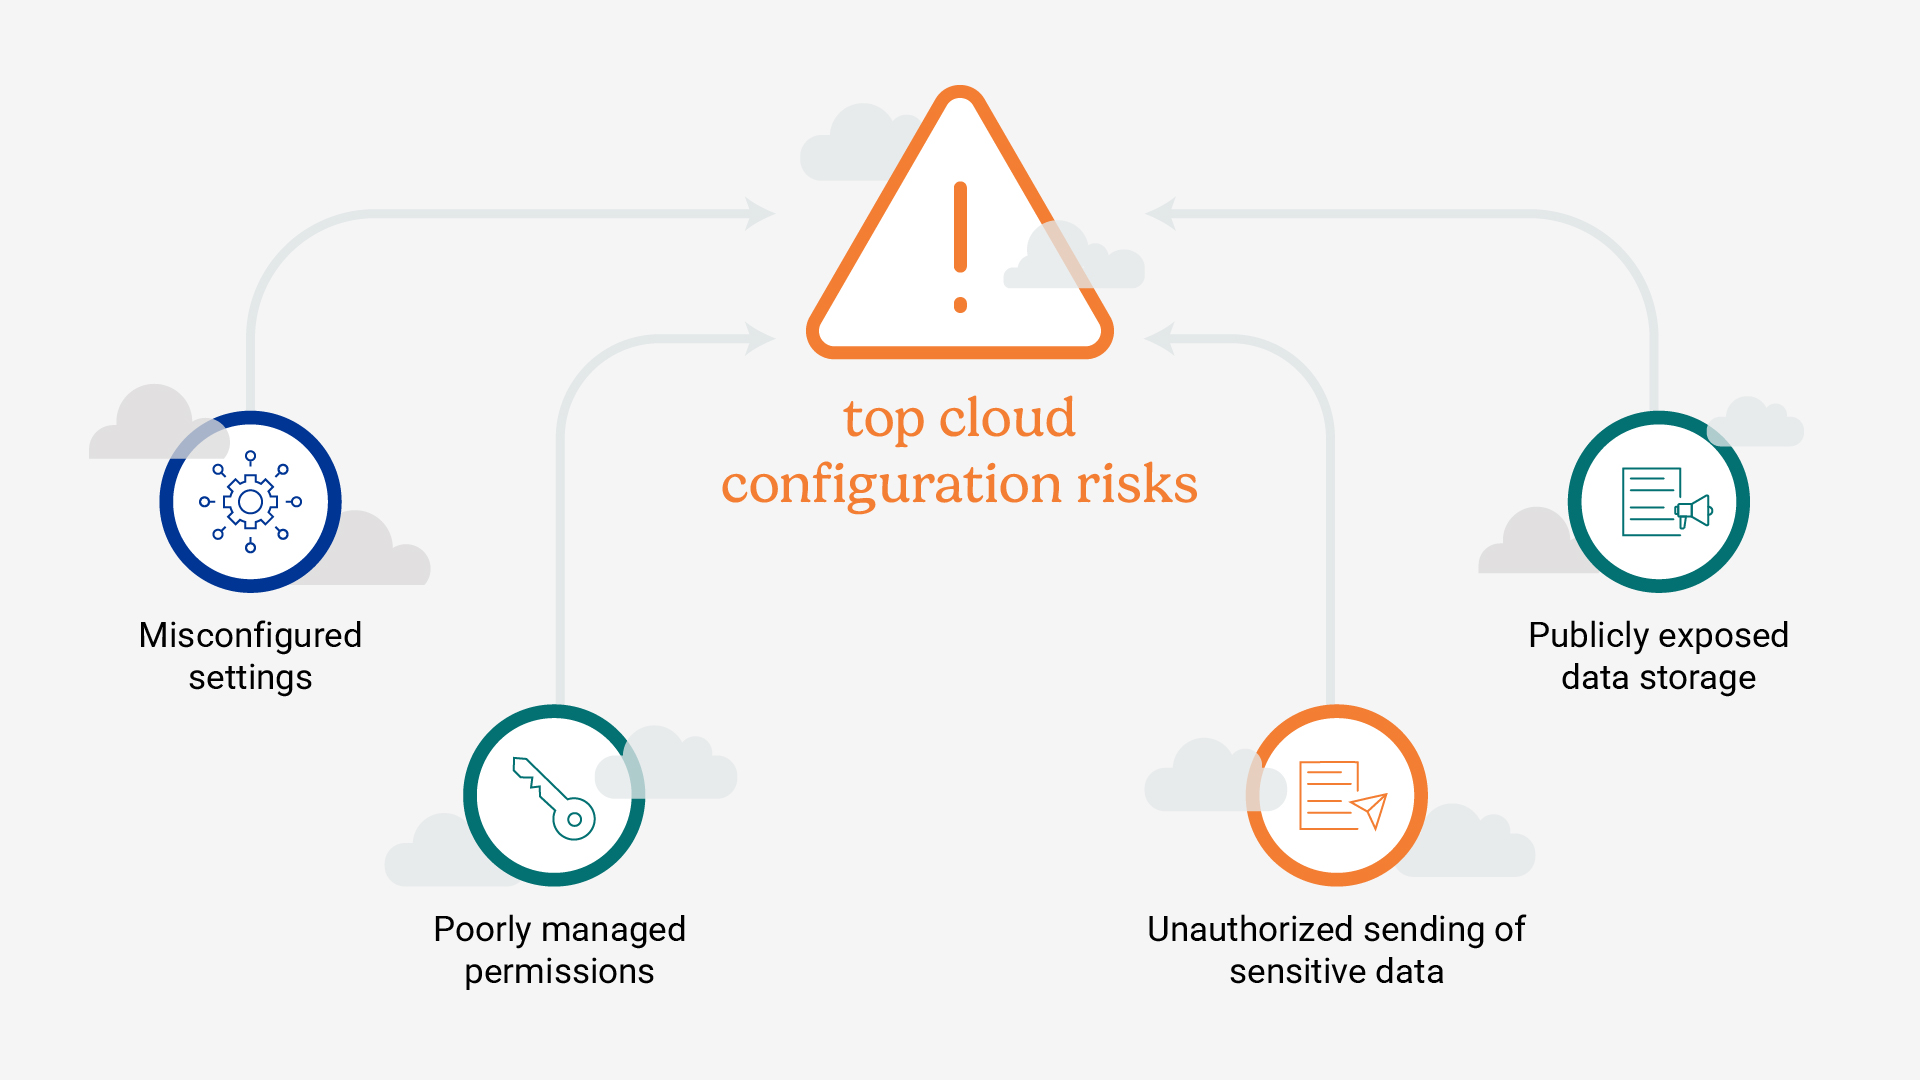
In 2025, nearly one quarter of cybersecurity incidents were caused by misconfigured IT or cloud security settings, a risk that continues to grow as organizations rely more heavily on SaaS platforms like Microsoft 365.
As cloud adoption accelerates, the attack surface expands, often outpacing the ability of security teams to keep configurations aligned with best practices. The result is a growing gap between how cloud environments change and how often their security settings are formally reviewed.
That reality sits at the center of a recent alert from the Cybersecurity and Infrastructure Security Agency (CISA), which warned that improper Microsoft 365 configurations have already led to real world compromises, including a cyberattack against a healthcare organization triggered by cloud misconfiguration. Healthcare organizations, in particular, remain prime targets for cybercrime.
Cloud platforms change faster than most organizations’ governance, audit, and risk management cycles. New features, default settings, and security controls are released continuously, often without leadership awareness or formal review.
Industry research shows that more than half of cloud breaches are linked to configuration drift over time. These issues don’t arise because cloud providers are insecure. They arise because configuration decisions are often:
Over time, small gaps compound into meaningful exposure.
Microsoft 365 is embedded in daily operations for most organizations. Email, file sharing, collaboration, identity management, and data storage all live within a single ecosystem, making it both powerful and vulnerable.
CISA has emphasized that improper configuration of cloud security controls has already resulted in actual compromises, prompting federal mandates to harden Microsoft 365 environments using secure configuration baselines.
Key risk factors include:
For many organizations, Microsoft 365 contains their most sensitive data, yet its security posture has never been independently evaluated.
A cloud security evaluation focuses specifically on how cloud services are configured today, not how policies are written or whether controls exist on paper.
An independent third-party team performs cloud security evaluations by comparing an organization’s Microsoft 365 (and other cloud platforms such as Azure, AWS, and Google Cloud) against Center for Internet Security (CIS) benchmarks, which reflect consensus driven best practices developed by the global cybersecurity community.
CIS Benchmarks are publicly available, regularly updated, and widely regarded as the industry standard for secure configuration across major technologies.
A typical cloud security evaluation includes:
Engagements are efficient, often requiring only one to two days of technical review, and culminate in a leadership ready report.
Evaluations frequently uncover settings that were never intentionally chosen by leadership, including:
For organizations operating under privacy regulations, such as healthcare entities or businesses subject to California privacy laws, these gaps can create compliance exposure alongside cyber risk.
As cloud platforms introduce new capabilities and settings on a regular basis, security configurations should be revisited with similar discipline. We recommend:
While internal IT teams should regularly reassess configurations, periodic external evaluations provide leadership with an objective view of current exposure and help determine which issues deserve immediate attention. Without these reviews, unexamined cloud configurations can increase security risk.
Elliott Davis helps organizations take a more disciplined approach to cybersecurity by providing independent, practical assessments of cloud and technology risk. Our services include:
Together, these services help organizations move beyond point in time visibility to a more consistent approach to identifying, prioritizing, and addressing risk. Our cloud security evaluations give leadership an objective view of current configurations, highlight gaps against recognized best practices, and outline clear, actionable steps to reduce exposure before issues become incidents.
Contact us today to get started.
The information provided in this communication is of a general nature and should not be considered professional advice. You should not act upon the information provided without obtaining specific professional advice. The information above is subject to change.
Healthcare organizations remain a frequent target for cybercriminals because patient data is valuable and clinical operations are highly sensitive to downtime. As healthcare systems become more dependent on connected technologies, even a temporary outage can affect patient access, care delivery, operational performance, and regulatory obligations. Ransomware groups understand these pressures and often exploit them to increase leverage during an attack.
A recent high-profile cybersecurity incident offers a clear example of how a cyber event can affect day-to-day healthcare operations. According to public reporting, the malware-related disruption affected systems supporting healthcare delivery, resulting in impacts to communications, patient-facing services, physician offices, imaging locations, and elective procedures while recovery efforts were underway.
For healthcare leaders, cybersecurity is closely tied to business continuity, operational resilience, reputation, and patient safety. The challenge is not simply preventing attacks, but maintaining critical services and supporting patients when key technology systems become unavailable.
Modern healthcare delivery relies heavily on technology. When critical systems are disrupted, the effects can quickly spread across the organization.
Disruptions can affect:
What begins as a cybersecurity event can quickly become an operational resilience challenge with implications for patients, caregivers, and community trust.
Healthcare organizations face growing pressure to protect patient data, support uninterrupted care delivery, and meet regulatory expectations. As cyber threats become more sophisticated and technology environments more complex, many organizations struggle to maintain visibility into risk, validate security controls, and prepare for operational disruptions.
Effective cybersecurity programs are built on a combination of risk management, governance, technical controls, and incident preparedness. Elliott Davis works with healthcare organizations to:
Contact us today to strengthen your cybersecurity posture and safeguard the care your patients depend on.